Stale vulnerability lists
A fixed CVE list shipped with a product is outdated within months; new vulnerabilities stay invisible.
NPM Security content
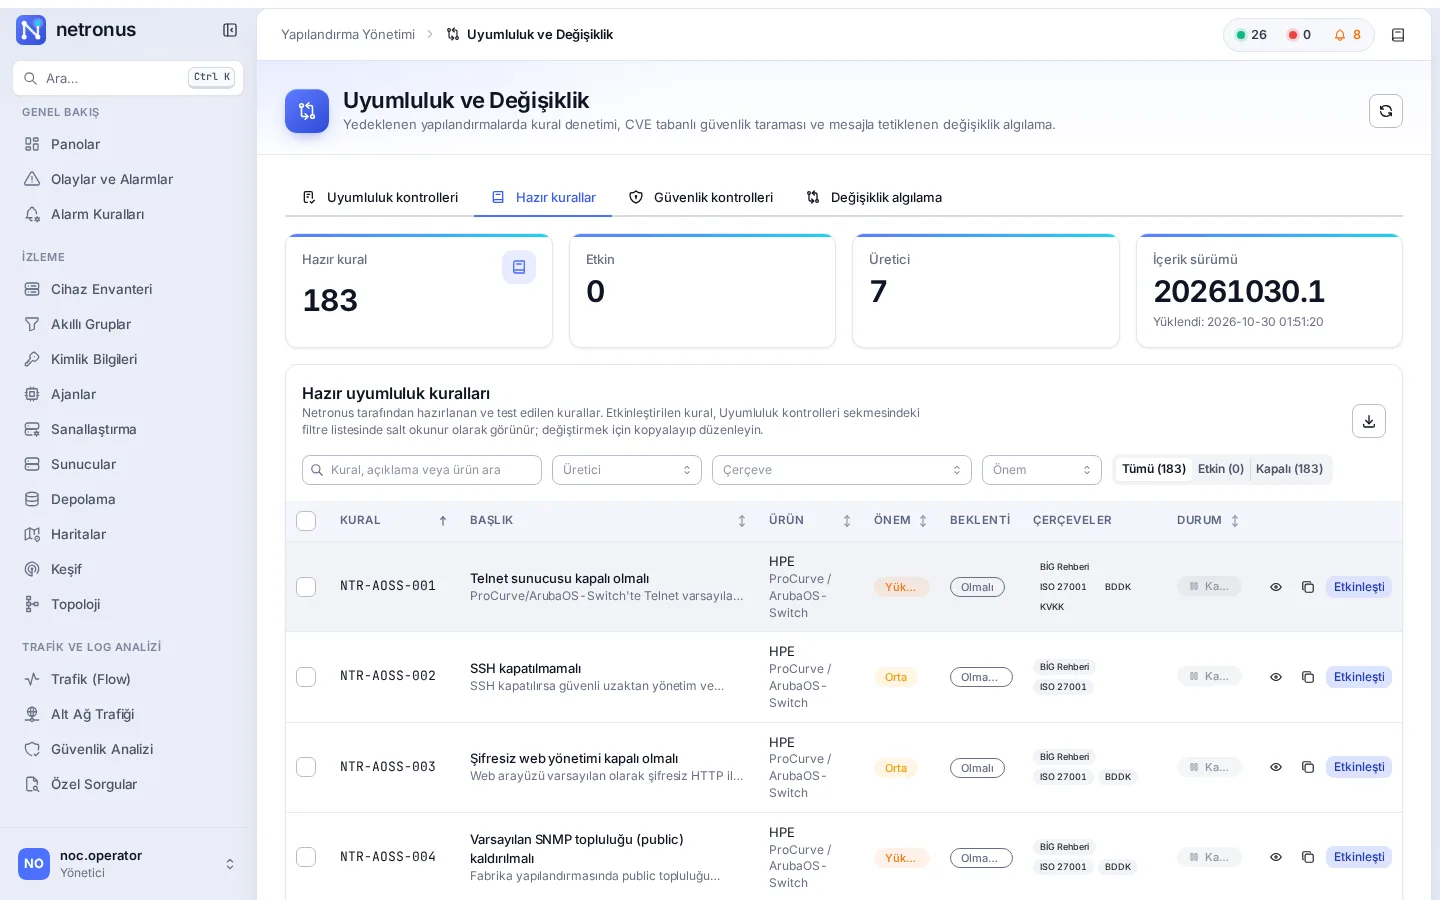
Netronus updates its vulnerability (CVE) database, ready-made compliance rules and change detection patterns every day, independently of the product release. Content is signed; organizations without internet access receive the same content as an offline package.
The problem
A fixed CVE list shipped with a product is outdated within months; new vulnerabilities stay invisible.
Separating actively exploited vulnerabilities from hundreds of CVEs takes time.
Checking configurations against corporate policy and regulation by hand is slow and error-prone.
The solution
Content is checked every day, and content whose signature cannot be verified is never imported. Device versions are evaluated automatically against affected version ranges; the whole inventory is scanned after every update and once a day.
Compliance rules reference and are mapped to the listed frameworks; they are not endorsed or certified by the framework owners. CIS text is not copied, only section numbers are used.
Capabilities
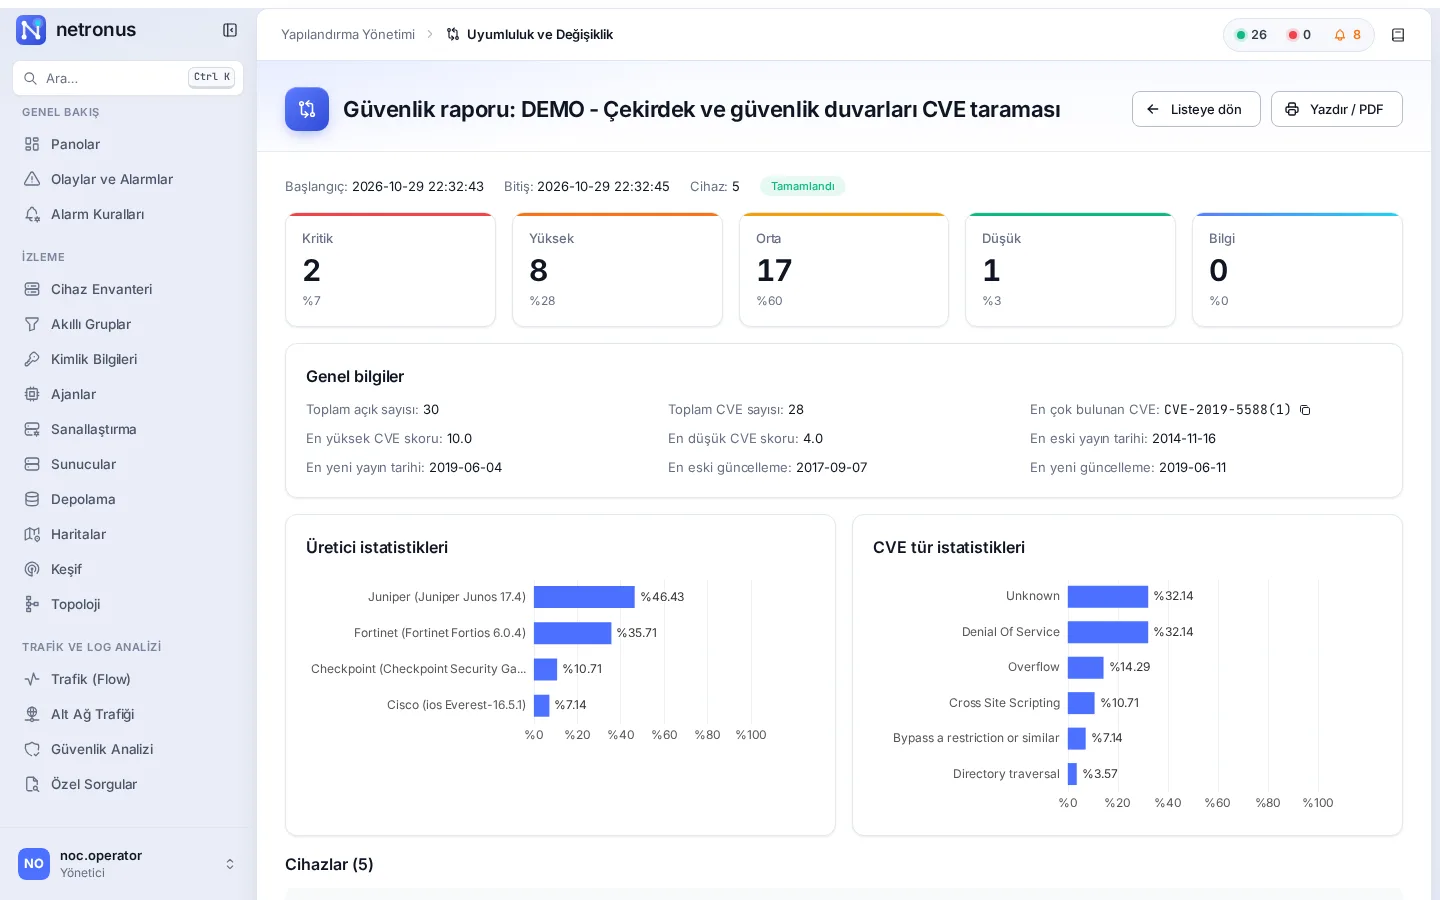
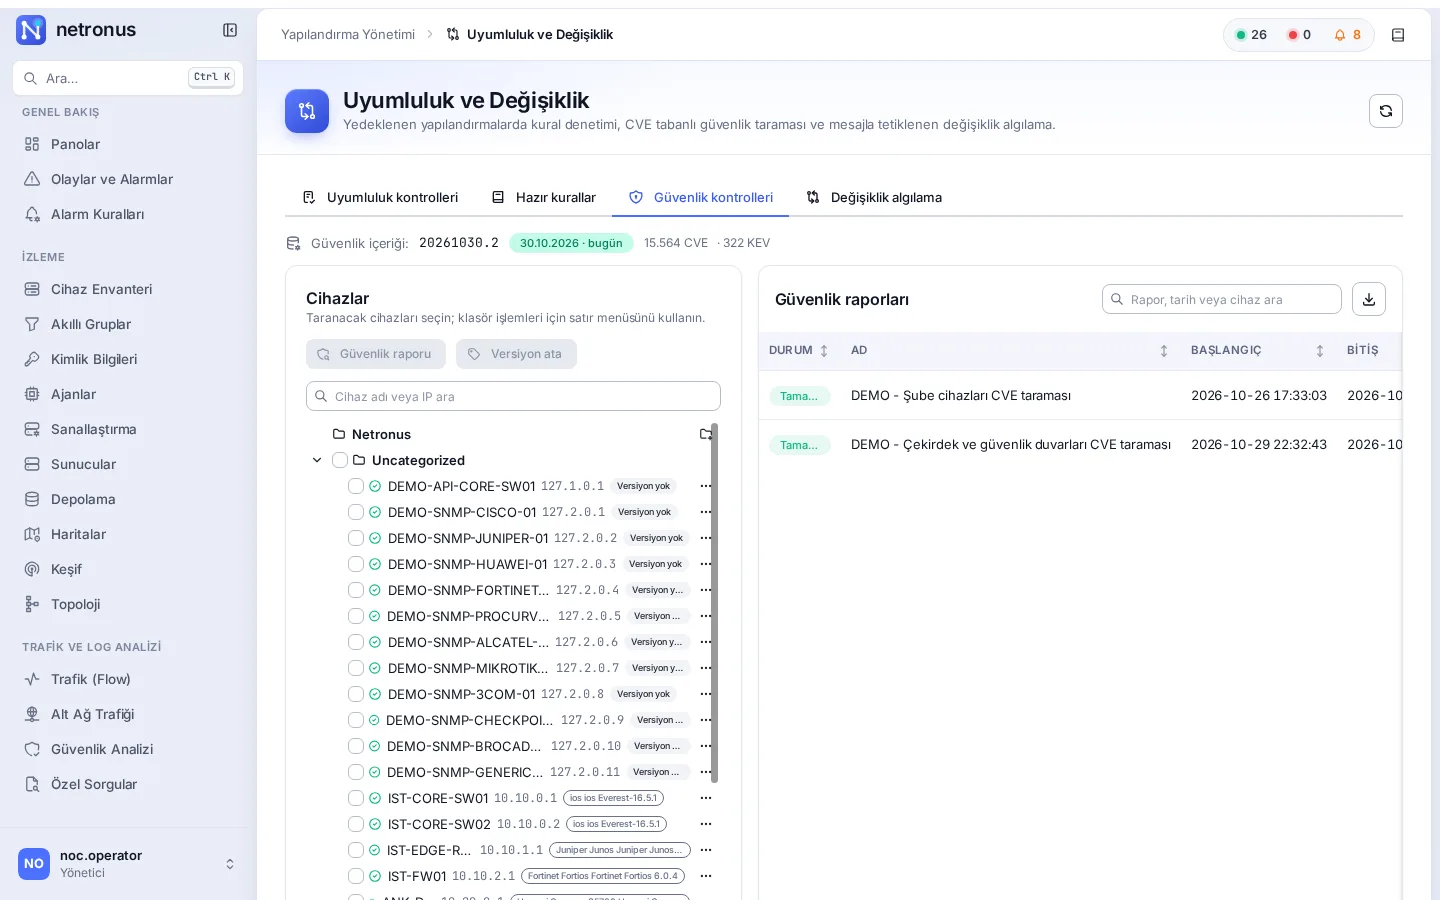
NVD, CISA KEV and EPSS data every day; KEV badge, EPSS probability and the fixed version when available in reports.
Assign a device version by hand or let Netronus detect it from the system description; affected ranges are evaluated automatically.
For Cisco IOS, ASA and NX-OS, FortiOS, Check Point Gaia, HPE Aruba switches, Huawei VRP, Juniper Junos and MikroTik RouterOS.
Rules are mapped to CIS benchmark sections, ISO/IEC 27001:2022 Annex A, the Turkish Presidential Information and Communication Security Guide, BDDK and KVKK.
Vendor patterns that spot configuration changes in syslog messages are updated with the content.
Every content package is signed; content with an invalid signature or an attempt to roll back to an older release is rejected.
Organizations without internet access upload the content package in the interface; the signature is verified the same way.
New critical findings appear on the Events screen and users with access to the device get a summary e-mail.
Screenshots
Technical summary
| Item | Detail |
|---|---|
| CVE sources | NVD, CISA KEV, FIRST EPSS |
| Updates | Daily and automatic; “Check now” on demand |
| Compliance rules | 183 rules, 9 platform families |
| Framework references | CIS (Netronus interpretation), ISO/IEC 27001:2022 Annex A, Turkish Presidential Information and Communication Security Guide, BDDK Information Systems Regulation, KVKK |
| Integrity | Signed content; rollback protection |
| Isolated networks | Signed offline content package |
| Notification | Event and e-mail for new KEV or CVSS ≥ 9.0 findings |
We will set up a demo on your network, show the screens with your own devices and prepare a quote for the modules you need.
Request a demoRelated
Back up device configurations with templates, compare versions, and audit them against your policies and known vulnerabilities.
Explore the moduleThresholds with duration and hysteresis, rate of change, forecasts, seasonal baselines; maintenance and dependency suppression. One engine for network, servers and storage.
Explore the moduleRuns on your own server. Signed updates; offline updates, licenses and content for networks without internet access.
Explore the moduleWe will set up a demo on your network, show the screens with your own devices and prepare a quote for the modules you need.