Local accounts on every device
Create, disable and authorise accounts in one place instead of maintaining users on each device.
Users, groups, NAS, accounting
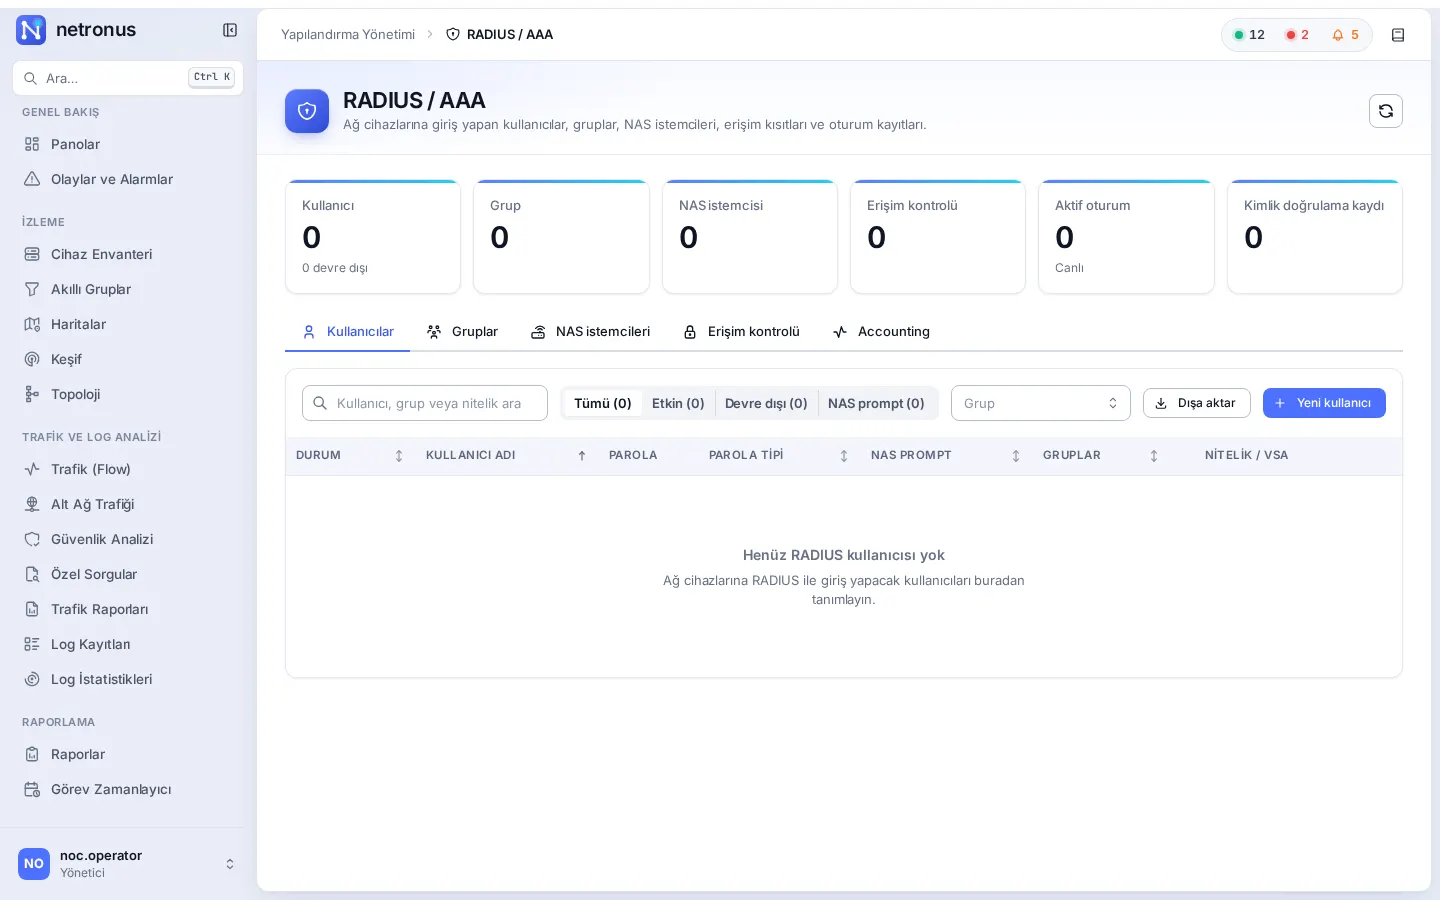
With its built-in RADIUS server, Netronus centrally manages the administrators who log in to your network devices. Users, groups, NAS clients, time-based access restrictions, accounting and authentication logs all live on one screen.
Problems it solves
Create, disable and authorise accounts in one place instead of maintaining users on each device.
Time-of-day windows, concurrent sessions, daily session limits and account expiry dates.
Successful and failed logins and session (accounting) records are searchable and exportable.
Capabilities
Password type, NAS prompt, group membership, attributes and enabled/disabled state.
Standard attributes and vendor-specific attributes (VSA) applied to every group member, e.g. Cisco privilege level.
Define the network devices that talk to RADIUS and their shared secrets.
Time-based access, concurrent use, daily session limit, session and idle timeouts.
Active sessions and historical session records.
Accept and Reject responses with user and timestamp.
Detailed feature list
All Netronus modules share the same inventory, the same permission model and the same interface. Any device you see here is one click away in every other module.
Feature matrixRelated modules
Back up device configurations with templates, compare versions, and audit them against your policies and known vulnerabilities.
Explore the moduleUsers, groups and a granular permission matrix; Active Directory/LDAP sign-in, signed automatic updates and on-premises deployment.
Explore the moduleCentrally collect, filter and live-tail syslog and SNMP trap messages, and keep them tamper-evident with time-stamped signatures.
Explore the moduleLet’s schedule a demo in your own environment or prepare a quote for your needs. Pricing depends on the number of devices and the modules you choose.