Logs scattered across devices
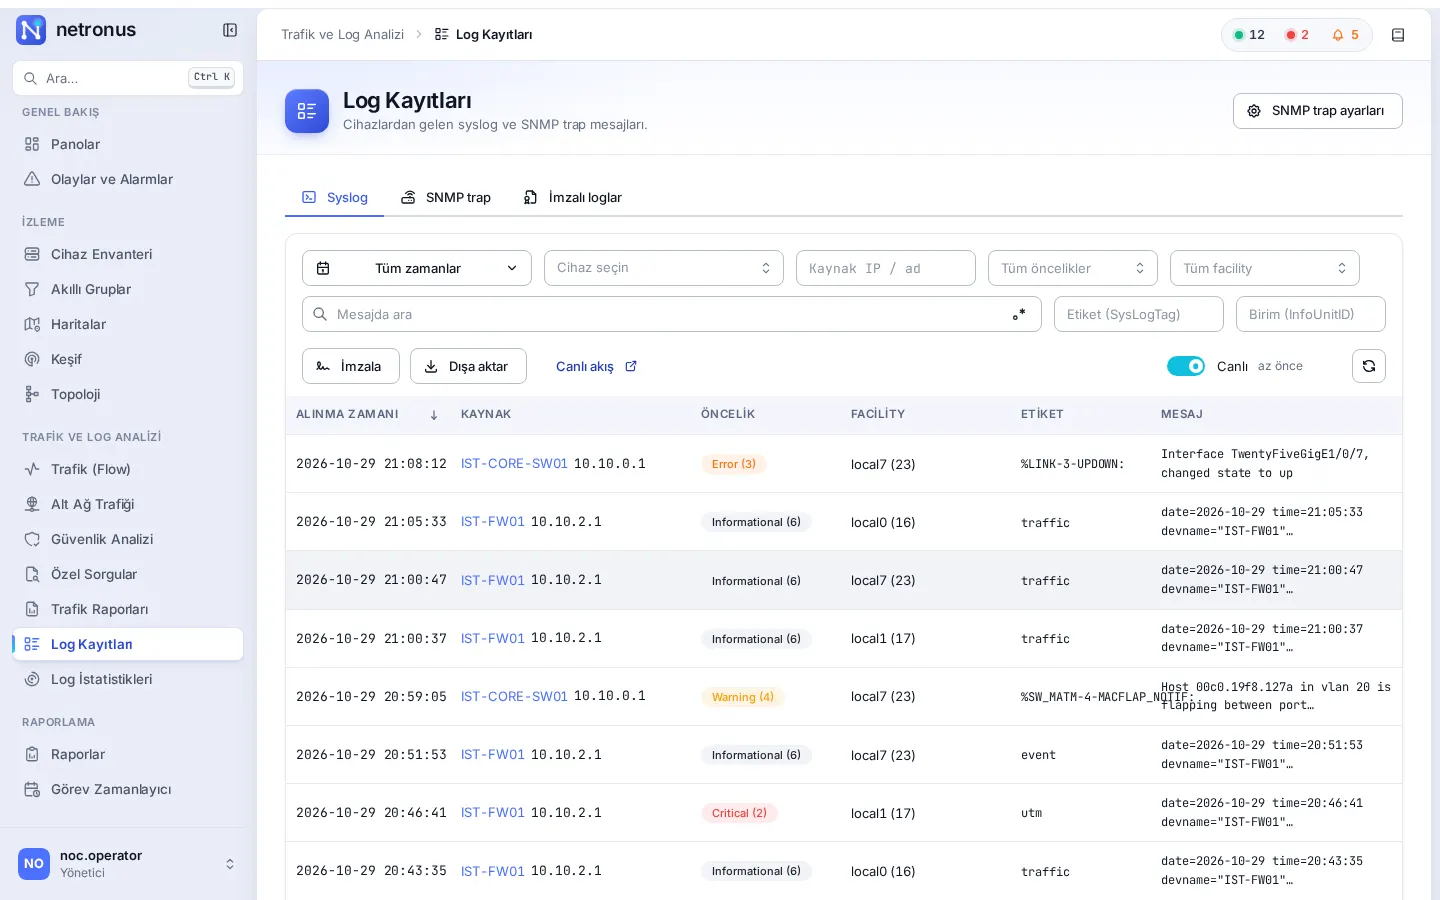
Instead of logging in to each device, every syslog and trap record is searchable on one screen.
Syslog, SNMP trap, signed logs
Syslog and SNMP trap messages from every network device land in one place. Filter by severity, facility, tag and message content, follow the live stream, and sign selected records with RFC 3161 time stamps to prove they have not been altered.
Problems it solves
Instead of logging in to each device, every syslog and trap record is searchable on one screen.
Signed log archives show that records have not been modified since they were signed, supporting Turkish Law No. 5651 log retention requirements.
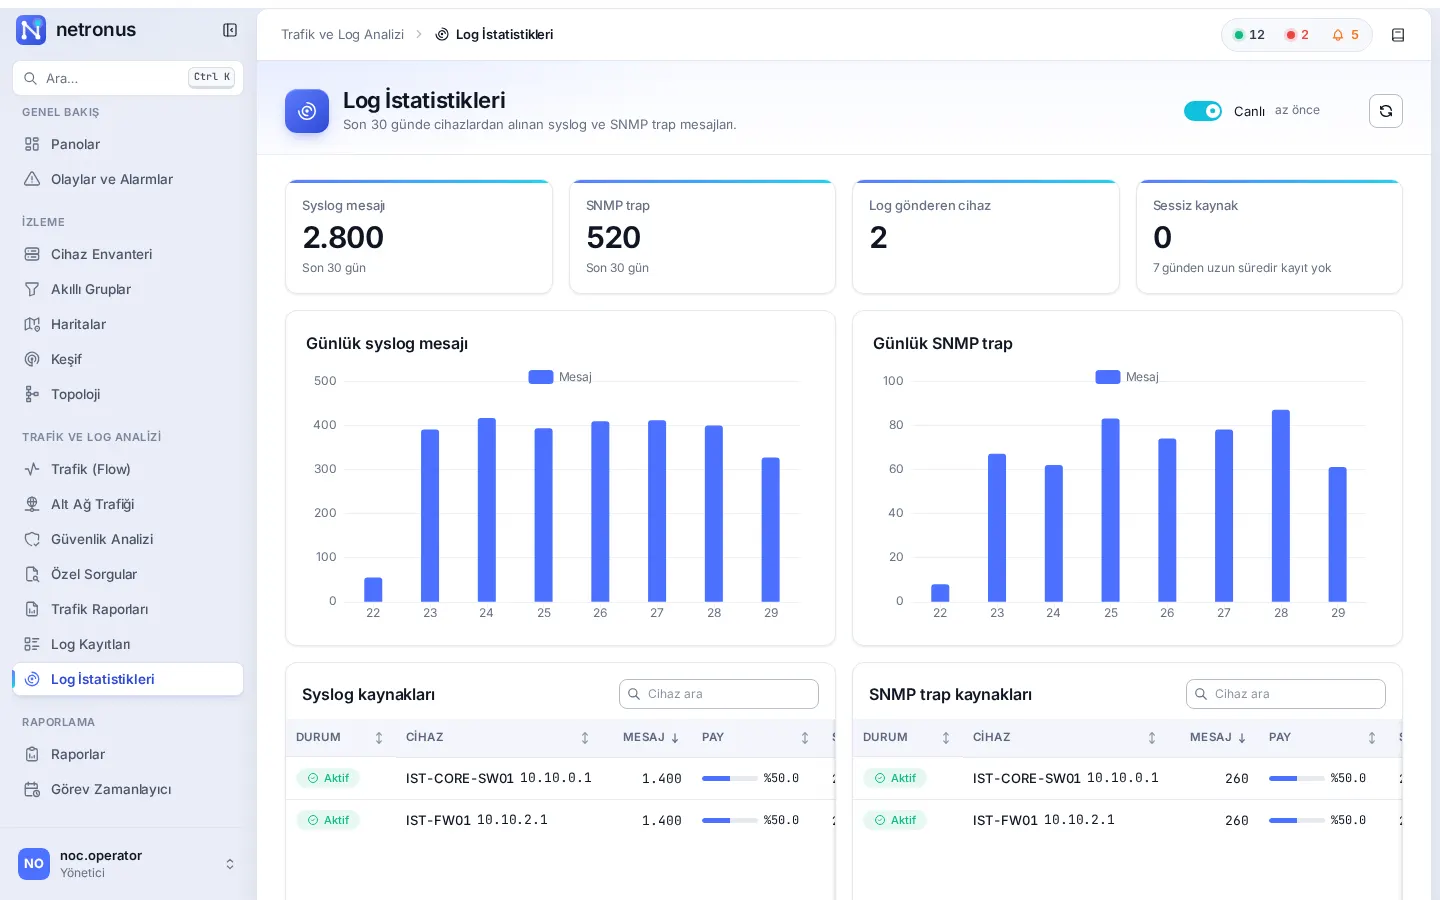
Sources that have stopped sending logs are listed separately on the statistics screen.
Capabilities
Stored with receive time, source, severity, facility, tag (SysLogTag) and unit; full-text search in messages.
Collect traps centrally; only traps sent with an allowed community string are accepted.
Watch incoming logs in real time; your filters apply in live mode too.
Sign filtered records with an RFC 3161 time stamp, either into a single file or one file per source. List and download signed archives.
Time stamps can come from the appliance’s own TSA or, where configured, from a qualified TSA such as TÜBİTAK Kamu SM.
Run signing jobs regularly with the Task Scheduler; the signing window is counted back from each run.
Daily syslog and trap counts for the last 30 days, share per source device, and silent sources.
Bind a specific log or trap message to an alarm rule, or use it to trigger configuration change detection.
Detailed feature list
Related modules
See who is using your bandwidth, with which application and toward which country, and catch malicious traffic and DoS patterns in your flow data.
Explore the moduleBack up device configurations with templates, compare versions, and audit them against your policies and known vulnerabilities.
Explore the moduleUsers, groups and a granular permission matrix; Active Directory/LDAP sign-in, signed automatic updates and on-premises deployment.
Explore the moduleLet’s schedule a demo in your own environment or prepare a quote for your needs. Pricing depends on the number of devices and the modules you choose.