Answer “the internet is slow” with evidence
Find the IPs, applications and ports eating your bandwidth within seconds of a bottleneck.
NetFlow, sFlow, IPFIX
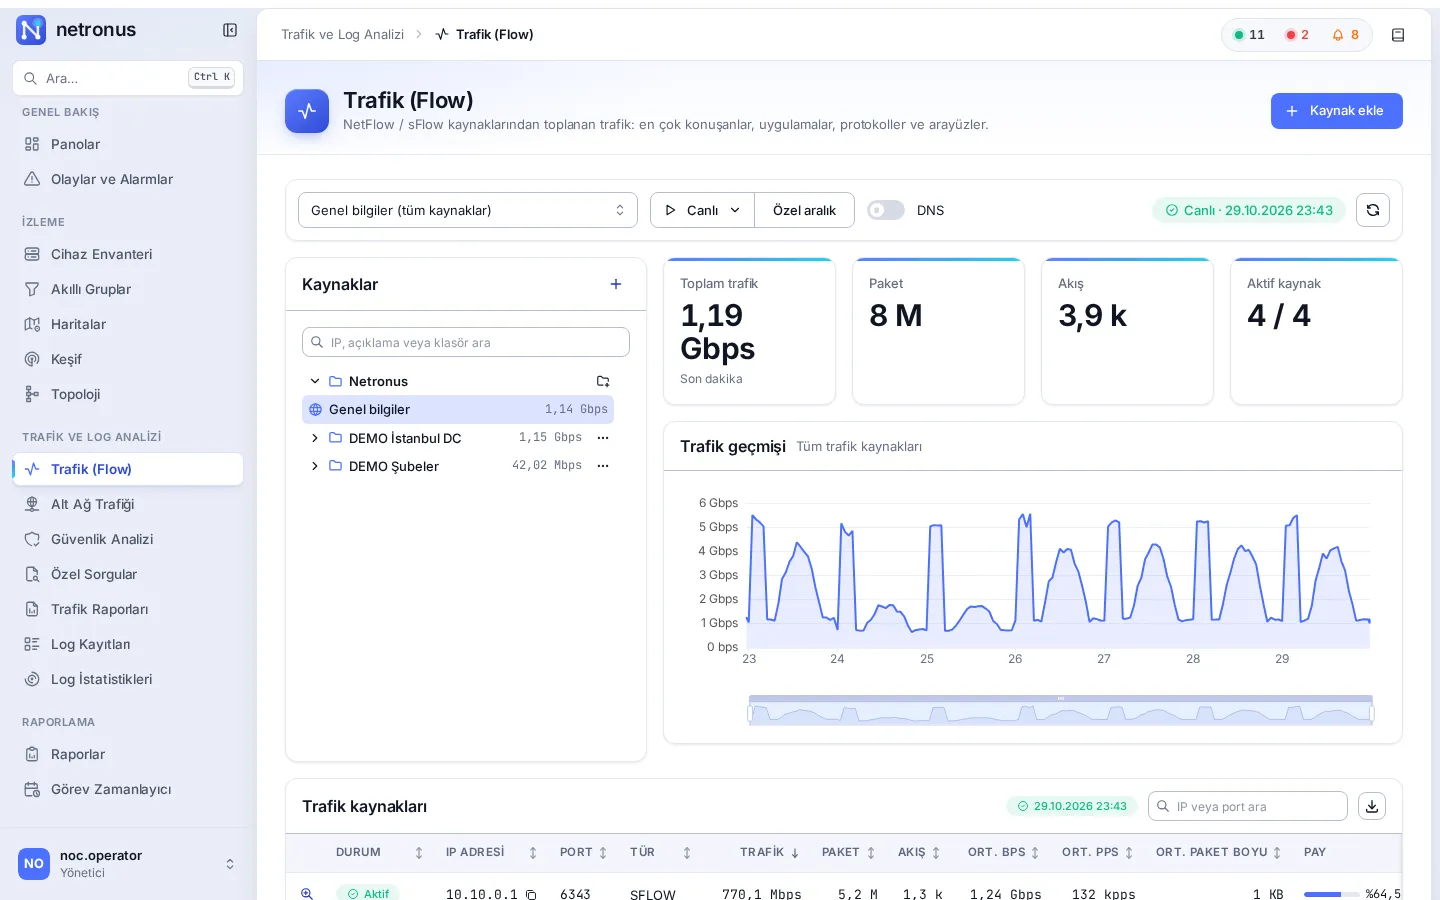
Flow records exported by your routers, switches and firewalls are stored by an nfdump-based collector on the Netronus appliance. Explore top talkers, applications, protocols, countries and subnets live or over any time range; subnets that exceed their thresholds and suspicious traffic are flagged automatically.
Problems it solves
Find the IPs, applications and ports eating your bandwidth within seconds of a bottleneck.
Per-subnet traffic history with thresholds; show which sites are growing with a report.
Traffic to blacklisted addresses, sources showing DoS behaviour and malformed packets in dedicated lists.
Capabilities
NetFlow v5/v9, IPFIX and sFlow; define the IP and UDP port of each exporter and track traffic, packets and flows per source.
Top flow statistics ranked by source/destination IP, port and interface.
Application and protocol breakdowns and per-country traffic, with optional DNS resolution for readable names.
Organise subnets into folders and set thresholds; subnets over their limit are highlighted on the map and in the list.
Malicious (blacklist) traffic, DoS detection based on a packets-per-minute threshold, malformed packets and unexpected ToS/DSCP values.
IP, network, network-to-network, protocol (TCP/UDP/ICMP), port and MAC based queries, with a live query preview.
Build flow reports with a wizard, re-run them and export the results.
Live mode or a custom time range, with traffic history charts and source tables.
Detailed feature list
All Netronus modules share the same inventory, the same permission model and the same interface. Any device you see here is one click away in every other module.
Feature matrixRelated modules
Centrally collect, filter and live-tail syslog and SNMP trap messages, and keep them tamper-evident with time-stamped signatures.
Explore the moduleProduce availability, interface, hardware, IP SLA and system reports from ready-made templates, calculate them over business hours, and run them on a schedule.
Explore the moduleContinuously monitor routers, switches, firewalls and servers over ICMP and SNMP, and alert the right people through the right channel the moment something breaks.
Explore the moduleLet’s schedule a demo in your own environment or prepare a quote for your needs. Pricing depends on the number of devices and the modules you choose.